How much Azure storage am I using for my DPM backup

Looking in your Data Protection Manager console you see that you are using X amount:

 
You then login to the Azure Dashboard and see that the same amount is being reported:


Switching to your Azure Account details you seen a different amount:


The reason is because of the amount of de-duplication that the Azure Cloud performs as detailed here:

Will the number of GB I am charged for be exactly the same as the amount of data I am backing up from my on-premises server?
No. There are several factors that will impact the amount of storage you are consuming in the Backup service including, but not limited to, compression ratios, the rate at which the data changes, and the number of backup copies you elect to retain in the service.

Cochlear Implant Processor upgrades on the NHS

This blog post is mainly for myself to use for future reference but hopefully it will be useful for any parents out the looking for information on the "rules" for when upgrades should be performed.

Map of Medicine - Paediatric cochlear implant - postsurgery
original file: http://hearing.screening.nhs.uk/getdata.php?id=23891
Mirror: https://db.tt/yliGfcxi

Information of use:
"20  Provide device upgrade when appropriate  
Quick info: Provide device upgrade (internal or external) when appropriate:
• cochlear implant centre to review:
           -patient records
           -staffing
           -training; and
           -financial implications
• cochlear implant centre to develop and roll out a plan with manufacturers, that includes:
           -training of staff
           -updating of programming software
           -availability of stocks and spares
           -availability of funds for new processors
• provide appointments for upgrading processors
• follow programming protocol
• provide reports to:
           -local professionals
           -referrer
           -general practitioner; and
           -family
• consider sequential bilateral"

D09/S/a - NHS STANDARD CONTRACT FOR EAR SURGERY: COCHLEAR IMPLANTS (ALL AGES)
original file: http://www.england.nhs.uk/wp-content/uploads/2013/06/d09-ear-surg-coch-impl.pdf
http://www.england.nhs.uk/wp-content/uploads/2014/04/d09-ear-surg-coch-0414.pdf
Mirror: https://db.tt/NwAcxYQ7
https://www.dropbox.com/s/ufvkcam53jq0xs0/d09-ear-surg-coch-0414.pdf

Information of use:
"Upgrade or provision of new sound processors on average at 5 yearly intervals, where available, in order to ensure patient access to up to date technology to maximise their hearing performance and subsequently outcome from the intervention."

System Center Data Protection Manager backup to Windows Azure

At %dayjob% we have been using Microsoft Data Protection Manager since 2007 and we are currently at DPM 2012 SP1 level (not the new R2 release).

One of the new features is being able to backup to Windows Azure as an option. We had looked at cloud backup in the past with Iron Mountain but at the time the pricing was prohibitive. Now with Azure we can store 5Gb a month in the cloud for free so it was worth dipping our toes in.

First things first is to create and account on the Windows Azure website – this takes all of 5 minutes and after handing over credit card details for any data over the 5Gb I was away.

Next step is to create the certificate that we are going to use to validate that the DPM server is trusted by Azure. The documentation goes on about using MakeCert.exe from the Windows SDK but as we have a Domain Certificate Authority I decided to try to use that instead. The problem was there appears to be no information from Microsoft on how to achieve this – in fact all documentation from Microsoft about getting Azure to connect to on-prem stuff is very poor IMHO.

First we have to create a certificate template that matches what you need according to the documentation:
http://msdn.microsoft.com/en-us/library/dn169036.aspx
http://www.microsoft.com/en-us/download/details.aspx?id=34608

• The certificate should be an x.509 v3 certificate.
• The key length should be at least 2048 bits.
• The certificate must have a valid ClientAuthentication EKU.
• The certificate must be currently valid with a validity period that does not exceed three years. You must specify an expiry date; otherwise, a default setting that is valid for more than three years will be used.

First thing was to create a certificate template that fits the above requirements. To do this I connect to our Domain CA and opened the Certificate Templates Console.

Within here I duplicated the Web Server template. And hit my first stumbling block. When duplicating the following screen comes up:


And being a modern man I though – lets use Windows Server 2008…..

That was a mistake, later when I was attempting to use the that certificate  I generated to connect to Azure I was getting errors that the certificate specified was not associated with any backup vaults:


After checking the Agent logs in: Program Files\Windows Azure Backup Agent\Temp\ CBEngineCurr.errlog
I saw the following line:

WARNING --->System.Security.Cryptography.CryptographicException: Invalid provider type specified.

This turns out to be a problem if the software (I’m guessing the Agent) can not understand the newer CA versions (http://serverfault.com/questions/475525/the-private-key-for-the-certificate-that-was-configured-could-not-be-accessed)

So at this point – choose Windows Server 2003 Enterprise.

Give the new Template a name and make a note of it – you’ll need this later.
Choose to Publish the Certificate in Active Directory


Under Extensions -> Application Policies add in client authentication (http://social.technet.microsoft.com/Forums/windowsserver/en-US/0e039144-1cf2-4370-a0a8-0f4e8ca4aff4/problem-issuing-web-server-certificate-with-enhanced-key-usage?forum=winserversecurity)


At this point you want to take a walk, or do something so that the Template has time to get replicated into Active Directory. Make a coffee/leave for the weekend this will all depend on the size of your Active Directory estate.

Now on the DPM server we want to create a certificate. To do this we are going to use certreq  (http://technet.microsoft.com/library/cc725793.aspx)

I created a request.inf file with the following parameters:

[NewRequest]
Subject = "CN=SERVERNAME.DOMAIN.local"
ExportableEncrypted = TRUE
KeyLength = 2048
[RequestAttributes]
CertificateTemplate="DPMCertificate"

Note that the Certificate Template to use is the one I told you to make a note of earlier.

Now from a command line: certreq –new
And select the inf file you created earlier
(if at this point you get an error “Template not found.  Do you wish to continue anyway?” then either your template name is wrong or its not yet available in the certificate authority.)
Save the resulting request file.

From the command line type: certreq –submit
Select your certificate authority (if applicable) and then save the resulting Certificate file.

This Certificate file is what we need to submit to Azure so remember where it is saved.

We might as well upload the certificate into the local machine personal store now so it appears here:


I now switched back to my Azure account and started to provision my cloud storage, this part I had to research a little to find which would be the best region to place the store at.


After a bit of Binging I choose North Europe based on http://www.robblackwell.org.uk/2011/04/12/azure-northern-europe-is-dublin-and-western-europe-is-amsterdam.html (as an aside you can see your fastest connection at a point in time by using http://azurespeedtest.azurewebsites.net/)

Click Create Vault.


After a bit of flashing, whizzing and popping we get a new backup vault under recovery services


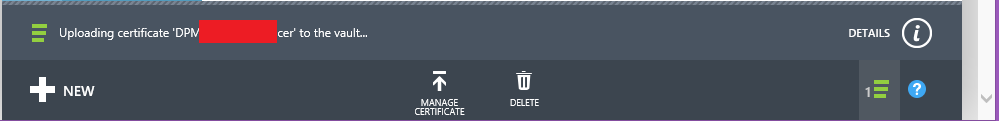
Clicking on the vault name you created earlier takes you to this page where you can upload the certificate (Manage Certificate):


We get another nice flashy upload graphic


If you certificate is invalid for some reason you’ll get an error which will help you to correct the problem and create a new one (I saw this a lot!):


Once you have a good certificate:


Now to download the DPM agent:


The agent can be downloaded from: http://go.microsoft.com/fwlink/?LinkId=288905

Now for some install screens (I'm sure if you've read this far you know how to click Next and Finish)


Once the Agent is installed and patched to the latest version (Windows Update). Then you can go on with the configuration within the DPM Console, click Online and then Register:


Click the browse button and any valid certificates are shown – select the one that corresponds to the one you uploaded (if need be compare the thumbprints)


Once the certificate has been compared to other certificates on Azure then your associated backup vault should then become visible:

(if at this stage you are getting errors then it could be proxy authentication  - check the agent error log again).

Now we get the chance to add in a proxy server (hey Microsoft – how about you do this earlier so we don’t get proxy authentication issues!)

Much like when we are setting up servers to backup we get the chance to choose how much bandwidth we give over to DPM:

We now need to choose where restores will go if/when we want to restore from Azure:

At this stage you create the Passphrase that DPM will encrypt your backup with before it is sent to the cloud. You can click generate passphrase and then Microsoft will helpfully give you a nice 36 digit GUID to use or you can generate your own by mashing the keyboard!
 

Success:
 
 
You now need to add online protection to a supported datasource within DPM and perfom a cloud backup. Once the backup is complete you can see from the Azure Management Portal the amount of data being held:
 
This information is also available in the DPM console:
 
I hope that someone finds this information helpful, the pricing of Azure Storage makes this a very attractive option for having an cold offsite backup and I look forward to more DPM workloads being supported in the future (hint SharePoint).
 
Comments as always are very welcome.
 
Update 22/10/2014: You no longer need to do the certificate creation according to this document: http://azure.microsoft.com/blog/2014/09/11/getting-started-with-azure-backup


Moving from a Mitel PBX to Lync 2010 (part three of three)

So we had reached the end of our journey, staff moved, Contact Center deployed. Time for the final push to migrate remaining analogue devices and switch off the Mitel.

For this part we continued with the company who started us on the Lync journey - Eurodata, but by now they had been consumed by Trinity Expert System who during the planning stage were taken over by Liberata. This caused some phone calls to confirm contracts being in place and existing bookings would be honoured but the scheduled time was met and we had support for the choosen weekend.

As we had Lync working with the Mitel/Dialogic setup we felt the route with least risk was to use a second Media Gateway (Sonus) to configure the ISDN onto which gave us the option of falling back to the Mitel/Dialogic configuration if towards the end of the maintenance window we had not got everything configured.

On the new NET UX1000 Sonus SBC 1000 the first challenge we encountered was configuring the number manipulation we had on the Dialogic (number re-writing on outgoing calls to present our non-geographic number for certain calls) and also to support what I like to think of as dynamic outgoing number rewriting but in getting suppliers to understand it can be refered to by any of these names:
  • ISDN Option 4 (noclip)
  • CLI Type 4
  • CLI No Clip
  • Presentation Number Type 4
  • CLIP No Screen
I'm including all of these here for the benefit of search engines as getting information was difficult to find in one place. The best non-technical description is from Ofcom:
Presentation Number Type 4
A presentation number available for the onward transmission of the originating number where a call breaks into a private network and breaks out again before termination, as in a DISA scenario. On the break out leg the number is generated by the user's equipment although it will have already been verified in consequence of having been delivered to the private network. To maintain the verification it is necessary to ensure that the number submitted by the private network is the number that was received.
Network providers wishing to offer a type 4 service will require a contractual commitment from customers that they will only submit CLIs that have been received from the public network. Unlike other types of presentation numbers, type 4 numbers may not always be diallable; this will depend on the nature of the number received from the public network
In Lync terms the best use of this is for Simultaneous Ring. An example is:
I've set my desk phone to SimRing my mobile as I'm waiting for an important call from the local Dominos. I don't want to answer a sales call though. The inbound call from Dominos (01553 777228) is to my Lync DDI (01553 667796) which SimRings my mobile (07775 560821). On my mobile I see the incoming call as 01553 777228. This is not possible without the ISDN option 4, at best you would see an incoming call from your DDI or maybe even the ISDN pilot number.


The upshot of all of the above was an extra few hours getting the Sonus box to do the same as the Dialogic, luckily the consultant we had has posted about the issue so hopefully that will help any future Sonus users.

Our final challenge was moving faxing over to the Lync Environment instead of having it hanging off the back of the analogue ports on the Mitel. We already have our remote site with analogue phone lines from Lync via a AudioCodes MP114 but faxing I had never been able to get working in a consistent way.

The solution was to have the AudioCode MP's homed twice, once on the Sonus box for fax (ISDN > Sonus > AudioCodes > Fax)


and also homed in the Lync topology for analogue voice (ISDN > Sonus > Lync > AudioCodes > Analogue Voice)


After a ream of paper and many many test calls we had a stable solution for faxing (100% success rate).

Late night Sunday we had everything in place, so I sent an email to all staff letting them know we had completed the works and went home. Monday morning came and my IT Support mantra came into play - "If you do your job properly, no one will know you have done anything."

The only fly in the ointment was the Dialogic Removal - we had left if powered on and in the Lync Topology just in case the was any major problems so after 12 hours of running on the Sonus I powered it off, and the following happened, my lesson, remove things from the Lync Topology before powering them off.

So after 7 years of faithful service it was time to:


Thanks for reading.


Moving from a Mitel PBX to Lync 2010 (part two of three)

By April 2013 all staff had been moved over to Lync 2010 Enterprise Voice and we started to look at the options for a Contact Center replacement.

After looking at a few of the different offerings in the market place we actually settled on what we had: prairieFyre for Lync (the Mitel 6100 is written by prairieFyre and then rebadged).

After placing the order with Koris (our implementation partner for the Contact Center rollout) Mitel then came in and purchased prairieFyre! We have had assurances that the product will not disappear though and that it will be marketed as part of the MiVoice lineup (edit 24/7/14 - looks like they kept their word).

As we standardised in the Contact Center we used our yearly PC refresh to prep new PC's for all of the Contact Center staff, the idea being that on cut over day we would unplug all PC's and phones on desks and plug in the new PC and new Jabra Pro 930 devices:


Whilst testing the solution we hit the following bug "AVMCU does not support DTMF in Lync 2010 Server or Office Communications Server 2007 R2" this was a massive issue for us as our legacy call recording solution injected DTMF tones into the call to stop and start call recordings to protect us from fraud and to comply with the PCI DSS requirements. After discussions with the supplier we felt that the best option was to source a new Lync Compatible call recording solution for those staff that take card payments. After researching the market and deploying a couple of POC's we choose Verba as the solution. One of the most interesting parts of their solution is what you can record depending on where the software is installed. We choose to install on the Mediation Servers which in our environment was the Front End Pool as this felt the least risky option - prairieFyre already changes the flow of calls so we were uncomfortable with two products potentially competing!

Go live was nice and smooth with the cut over happening on our quietest day of the week, staff coped well but after a few days were complaining about the ring tones in the Jabra being too quiet to hear. To compensate we found the ideal solution in Busylight, its a USB Lync Qualified Presence indicator with ring tones built in meaning that you can set the audio controls on the PC to whatever you want (muted) separate from the ring tone and light to notify you/others of incoming calls and presence state.


Once rolled out we were then ready for the final challenge - migrating fax machines and powering off the Mitel.

Moving from a Mitel PBX to Lync 2010 (part one of three)

I’ve worked at %dayjob% since July 2006, where we have a Mitel 3300. At the time this was amazing – digital to the desktop, everyone with their own DDI, Voicemail and the ability for an end user to setup hot keys themselves – it was THE FUTURE!

February 2007 saw the Network Admin and myself visit Nottingham for a Microsoft Technet Roadshow. The Microsoft Presenters were Eileen (Twitter), Darren (Twitter), Steve (Twitter) and James (Twitter) – the presentation that stood out was of Office Communication Server 2007 and a live demo with Tayside Fire and Rescue who used OCS for audio communication as well as IM and presence. Coming back to work I started to enthuse about what the IM and presence features for OCS would bring for us and how it would enable us to work smarter. We worked up a small skunkworks server in the ICT team using a Technet installer which worked well for us but we never pushed further due to other commitments.

The use of OCS throughout the organisation was still a dream of mine which after much selling to other members of the team and to the management team we succeeded in getting budgetary approval for the rollout of OCS 2007 R2 to all users for IM, presence and P2P audio/video. This work was carried out with PostCTI and in a short space of time we had every member of staff enabled. One side note here is that we provided training to groups of staff and at the end of each training session we gave away some gifts: a webcam and headset (all OCS certified so plug-and-play) and a packet of Jelly Belly Beans to emphasises the presence jelly beans in OCS and Outlook – people love sweets!

One thing that we had not anticipated was how the scheme managers (a single person looking after a sheltered scheme - an old peoples home in common parlance) would take to video conferencing, we worked out that this was because they would only get together with their colleagues at the monthly team meetings and so this gave that face to face feeling that other staff got in the main offices.

In December 2010 we launched the our Contact Centre – this was designed to be one stop shop for the majority of calls that we took and was built on the Mitel 6100 system. This was a great success and the use of OCS jelly beans to check for the status of people before calling them was part of the procedures that each agent would use.

Over time we got to a standardised desktop (Windows 7 and Office 2007 throughout) and OCS was looking a bit tired as it was based on Office 2003 non-Ribbon layout. The Mitel 3300 was starting to get tired too so based on the success of OCS we started to explore using it as our phone system. We chose Eurodata systems to help us get to this stage and after a very fast Proof-of-Concept stage we rolled out Lync 2010 to the ICT team as our phone system in a behind the PBX configuration (ISDN to Mitel to Media Gateway to Lync).

After rolling out to ICT we had an urgent request for a senior member of staff to be able to work from multiple offices with the same phone number. Using the Mitel system this would have been…… uhhhh….. messy and expensive. Moving him to Lync seemed like the most obviously solution, especially as we had deployed the Lync Edge server role and had Outlook Anywhere running too.

Over the next few years we migrated all staff to Lync 2010 Enterprise Voice for their phone services. We appeared to be ahead of the curve on the migration as we let our staff CYOD (Choose your own device). The device choice was limited to:

Polycom CX300

 
Blackwire C320-M
 
Blackwire C310-M
Jabra UC Voice 250 MS
Jabra PRO 930USB


Share photos on twitter with Twitpic One insight is that (unless there was direction from a manager on device) people would say they want a desk phone but then after a few weeks they would see the advantage of having a wireless headset and ask to change. In that way our original order of CX300's got moved to a new team every few months and we would start the process again!

Other area's that got Lync were our carpentry office who use a Bedlam Siren Caller on an analogue phone line and all our remote sites who use Remote App’s for the majority of their ICT Services. So by the end of April 2013 everyone was “Lync’ed Up” – all that is apart from the Contact Centre Team.


Updated with device choices 29/11/2013 & 06/02/2013

Unused Media Gateway stops Lync 2010 Response Group calls

Over the last weekend we removed our legacy Mitel PBX and replaced our Dialogic Media Gateway with a Sonus SBC 1000.

The Dialogic was left in place but does not appear in any call routing with the idea if we had a massive problem we at least had the infrastructure in place to start failing back.

Today I came back from a meeting and thought to myself “I’ll power off the Dialogic and the Mitel box now”

So I did.

All seemed to be fine – no user complained.

An hour later an external call came into our ServiceDesk Response Group. Which I was not able to pick up. Looking on the Monitoring server we had the following:

10001 - Gateway did not respond in a timely manner (timeout)

Powering the Dialogic on fixed the problem (We could all pick up Response Group calls again).

I have since removed the Dialogic from the Topology and powered it off and Response Groups are still working.